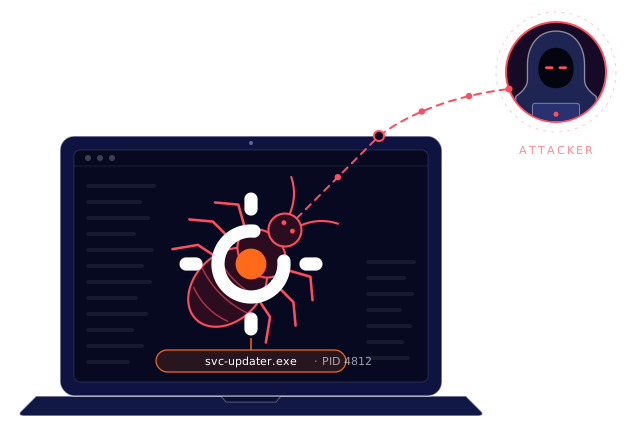
Blocking stops the request. It doesn't stop the malware.
A DNS block hides the symptom while the infected software keeps running and calling out. DNSEndpoint names the process behind each malicious connection, so your team can remove it at the source, without depending on an XDR.
One agent, two modes
Choose the mode per device, or apply it to whole groups at once.
See everything, touch nothing
Runs passively. It does not intercept traffic; it watches DNS activity on the device and pinpoints the software behind every malicious connection.
Detect it and stop it
Everything in Monitor mode, plus DNS-level blocking on the device. Malicious connections are stopped before they reach the internet, wherever the device is.
Find the origin on every device
DNSEndpoint brings process-level visibility to DNS security, on its own, across every endpoint you manage.
Process detection without an XDR
One agent for every device
Windows and macOS
Choose the mode per device or per group
There's more to discover !

Hey, I'm Sensei
I can walk you through everything about DNSEndpoint. What's on your mind?