ThreatOrigin

Your all-in-one threat hunting platform that just plugs in

Go from zero to hunting in minutes and get instant visibility across your entire network from a single platform

Day one impact on autopilot

This isn't just automation. It's expert-level intelligence. The ThreatOrigin comes with battle-tested scenarios and a data-specific AI, delivering an immediate boost to your security posture. From the moment it's connected, it empowers your team to focus on critical investigations with the unique ability to instantly query any event, past or present.
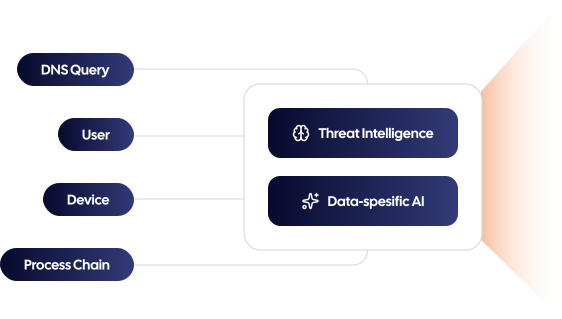
End-to-end threat hunting event chain from DNS query to process

End-to-end clarity, without the complexity

Other tools give you puzzles to solve. ThreatOrigin delivers the complete story. A single DNS query is just the beginning. Our platform instantly maps the entire event chain—from the query to the user, the device, and the specific process responsible. This end-to-end view, automatically enriched with our AI, threat intelligence, and your existing security data, gives your team the human-readable insights they need to hunt threats, without the complex setup.

THREAT HUNTING → KEY FEATURES

Break the barriers to effective threat hunting

The ThreatOrigin threat hunting suite is engineered to address the core operational failures of modern security programs, delivering clarity, efficiency, and demonstrable ROI.
Feature 1 illustration

Your tools don't hunt. Your people do.
Great hunters are rare, and burnout is real. ThreatOrigin acts as a powerful force multiplier, automating the manual, repetitive work of sifting through data. This frees your experts to focus their valuable time on high-impact investigations and strategic response, turning limited capacity into a scalable hunting operation.
Feature 2 illustration

Find the signal. Lose the noise.

More alerts don't mean more security. ThreatOrigin automatically validates incidents from across your security stack against our own data-specific AI and world-class threat intelligence. This dramatically reduces false positives and the alert fatigue that plagues most security teams, letting them focus on what matters.
Feature 3 illustration

Detect the unseen. Stop the unheard.

Modern attackers live off the land, using legitimate tools to avoid detection. By analyzing the entire DNS event chain for behavioral anomalies—not just signatures—ThreatOrigin uncovers the stealthy, malware-free intrusion techniques and command-and-control channels that traditional defenses were never designed to see.
Feature 4 illustration

Prove the value. Justify the spend.

Proving the value of threat hunting is no longer a challenge. ThreatOrigin delivers clear, actionable metrics on everything from newly identified security gaps to a dramatic reduction in SIEM license costs. It transforms a security line item into a strategic business advantage with a clear and demonstrable ROI.

There's more to discover !

Sensei

Hey, I'm Sensei

I can walk you through everything about ThreatOrigin's threat hunting feature. What's on your mind?