ThreatOrigin plugs into your central DNS and DHCP servers and, through smart integrations, discovers the users, hosts, and processes behind every query across your estate. You gain full DNS‑layer security and visibility for large, distributed networks in a fraction of the time of traditional DDI solutions, without deploying appliances or agents at every site.

Up to 95% reduction in
DNS EPS sent to SIEM

Ready SOAR playbooks
that cut false positivesand noise
instead of adding alerts

SOC investigations
up to 90% faster thanks to
correlated, scored events
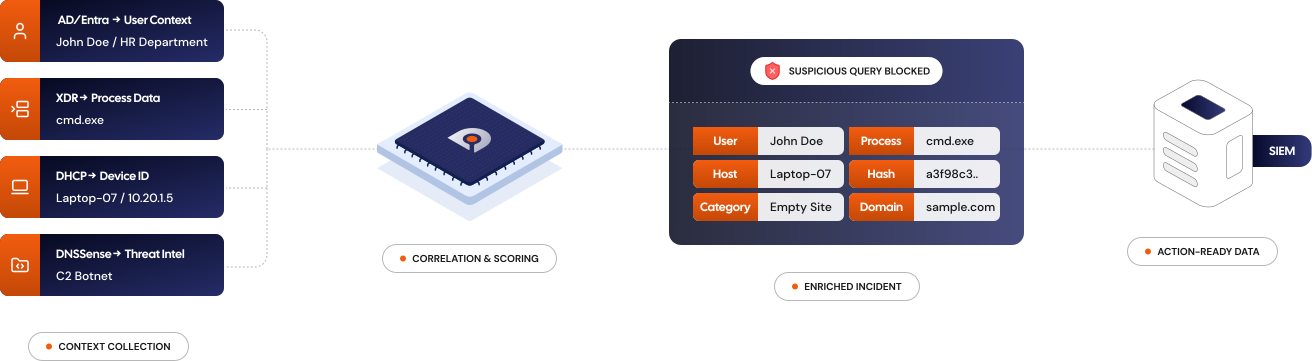
ThreatOrigin automatically correlates raw DNS signals with XDR process data and user identity before they reach your SIEM. SOC teams get a single, fully resolved incident timeline, allowing them to close cases in minutes without switching consoles.
Security that molds to your infrastructure
Stop re-engineering your network to fit a security tool. ThreatOrigin is built to adapt to your existing layers, identity providers, and operational workflows—delivering complete protection without the friction.
Simplified administration.
Identity-centric control.
Deep process visibility.
Layer-agnostic architecture.
There's more to discover !

Hey, I'm Sensei
I can walk you through everything about ThreatOrigin's adaptability feature. What's on your mind?