Finally, GDPR-compliant threat hunting without compromise
Most solutions face a hard trade-off: they skip user traffic to avoid compliance risks, leaving you with critical blind spots. Because they can't separate the threat from the identity, they often have to exclude both.
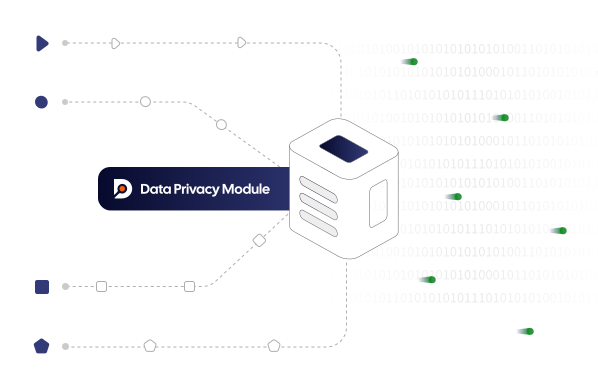
ThreatOrigin bridges this gap. Our on-prem Privacy Module processes full traffic data locally—giving you deep visibility into every signal—while keeping personal identities encrypted and isolated in your own environment.
Stay compliant without going blind
Get the full power of advanced threat hunting and AI inside your own environment, while personal data stays isolated and under your control. Your security teams keep the visibility they need to detect and investigate threats, and access to identities remains limited to your authorized privacy personnel.
Turn every alert into a fully resolved story
Connect every DNS event to the real device and context behind it, across any network topology. Let investigations move from a single signal to the precise endpoint—without exposing personal data.
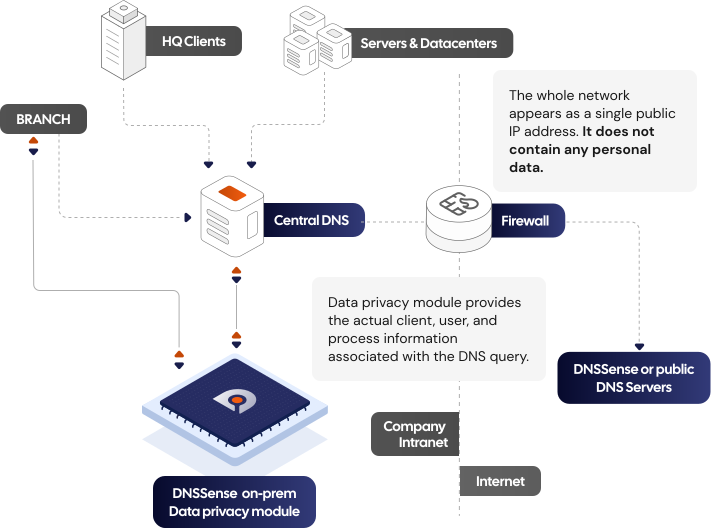
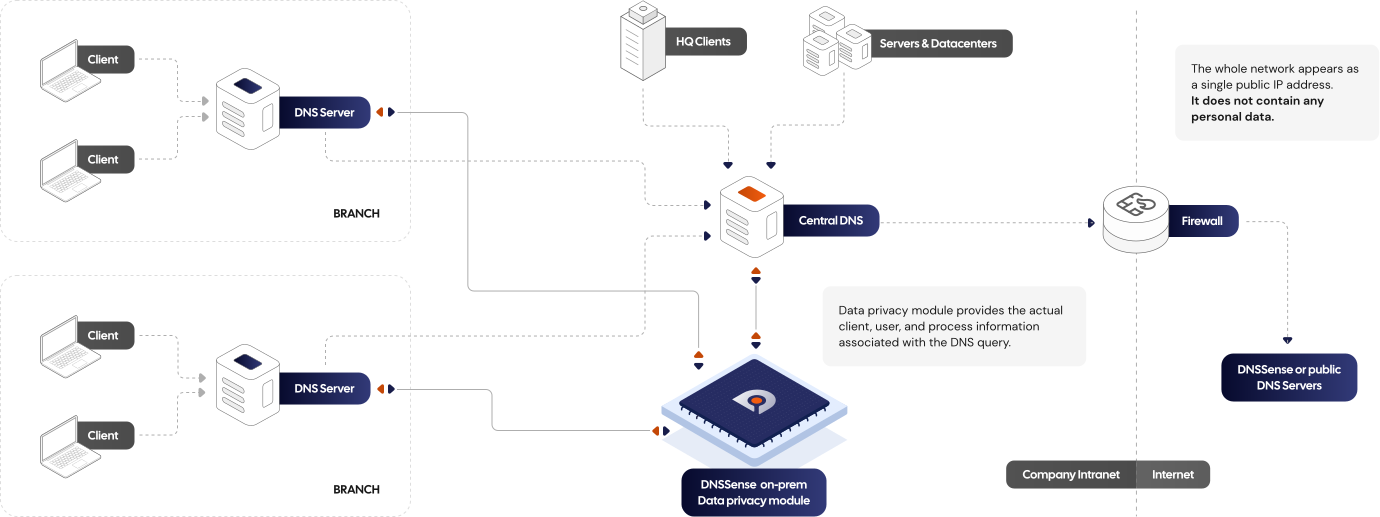
Engineered to solve the privacy-security paradox
It takes more than a policy to protect data. It takes deep visibility, seamless integration, and certified controls. ThreatOrigin delivers the complete framework for a secure, compliant, and efficient network.
Rich context, zero exposure.
Integrate seamlessly, operate instantly.
Certified trust, audit-ready.
Granular control, absolute governance.
There's more to discover !

Hey, I'm Sensei
I can walk you through everything about ThreatOrigin's data privacy feature. What's on your mind?